What we have learned at OpenShell applying formal methods to control AI agents — SkimNews
Get the Tech newsletter
Daily tech — startups, AI labs, chips, the launches that shape the next decade. Free.
- Nvidia's OpenShell team is using formal methods—specifically Microsoft's Z3 SMT solver—to mathematically prove that AI agent permission policies stay within operator-approved boundaries, even when agents combine multiple tools and credentials.
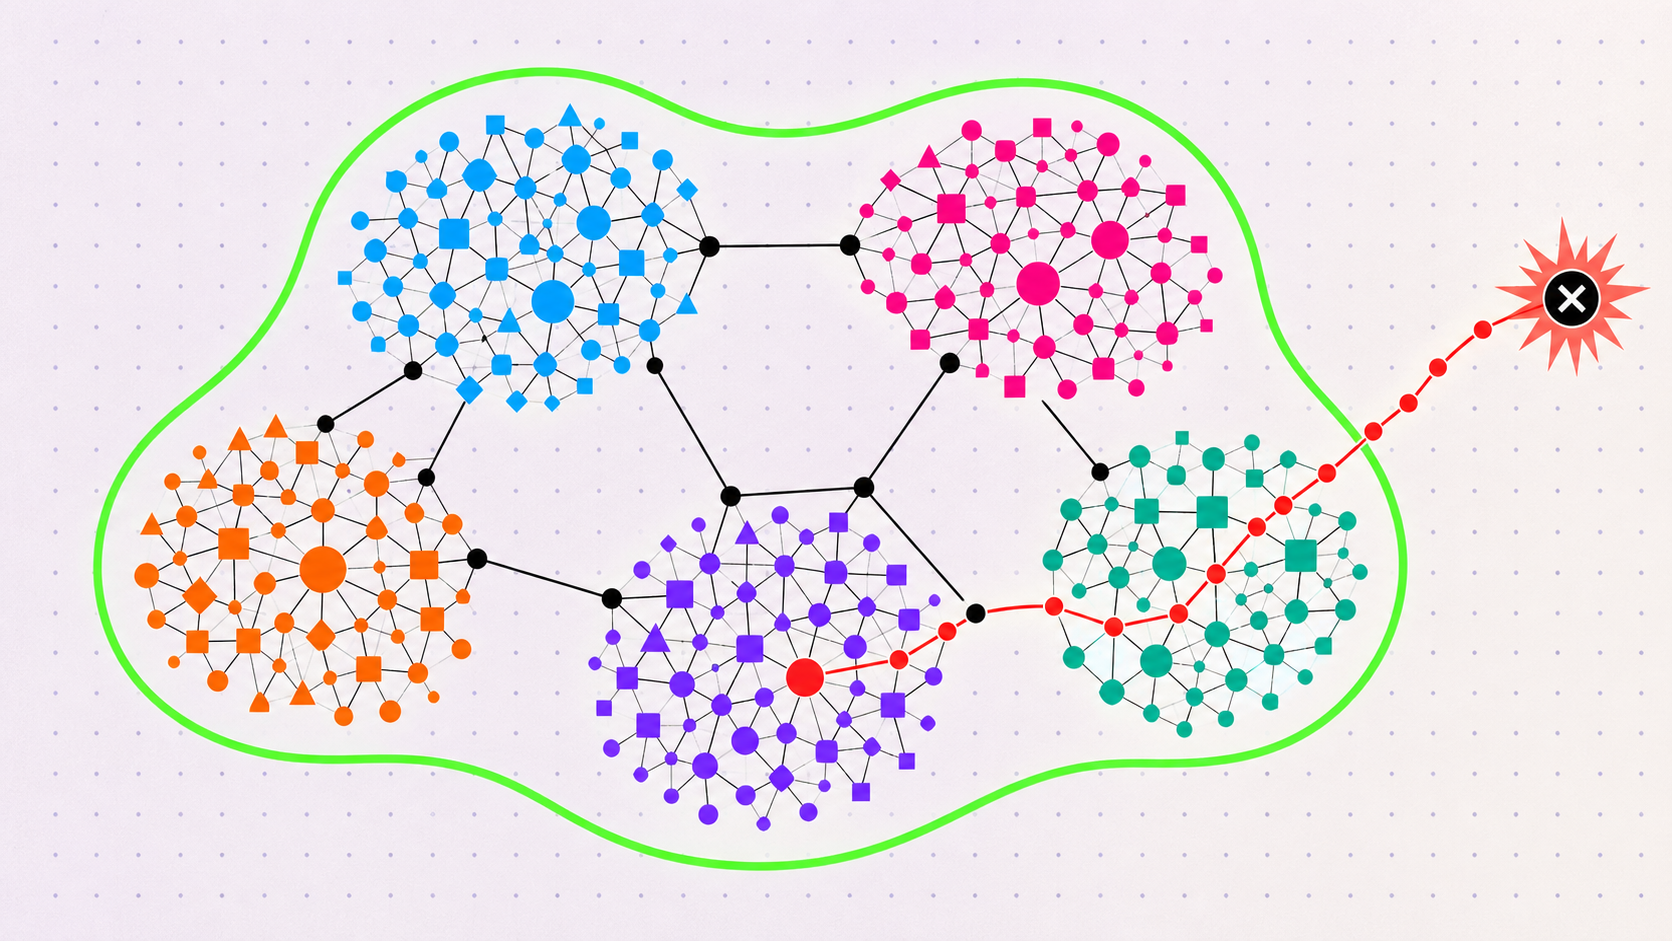
- A demo for Jensen Huang showed an OpenClaw agent bypassing a sandbox's layer 7 HTTP/REST inspection by combining its GitHub credentials with the git-remote-https binary over a wire protocol, exploiting a binary that had been approved only for cloning repos.
- The approach builds on AWS's Zelkova system, which team members built around 2016 with Byron Cook and colleagues to formalize IAM, S3, and EC2 policies as SMT formulas—a system now invoked billions of times daily.
- Formal proofs run in milliseconds with zero tokens consumed, contrasting with frontier labs' trusted-AI-reviewer approach, which the source says doubles compute costs and halves token throughput.
- The Z3 queries check whether a proposed policy's capabilities exceed a pre-approved reference policy's, encoding layer-4 network capabilities against layer-7 REST rules to catch the exact bypass class demonstrated in the OpenClaw demo.
- The article concedes formal checks lack contextual awareness—they cannot distinguish a throwaway repo from a production database—and are positioned as a complement to human or trusted AI reviewers rather than a replacement.
Why it matters: As organizations deploy hundreds of agents on long-horizon research tasks, the only scalable guardrail today is probabilistic AI review, which doubles compute costs. OpenShell's deterministic Z3 proofs offer token-free verification in milliseconds, but the source explicitly notes they cannot understand context, so they only work alongside—not instead of—human or AI reviewers in sensitive deployments.
Ask SkimNews